Technical security
Penetration testing, code review and architecture work for applications and engineering teams.
Code Guardian builds focused products for security controls that should not require a stack of tools and a team of specialists to operate.
Many important controls still require specialist knowledge, several tools, implementation projects and ongoing maintenance. We reduce that burden with software that does one job clearly, backed by experienced security practitioners.
Our products make proven security capabilities easier to adopt, operate and maintain, without needing a large security team.
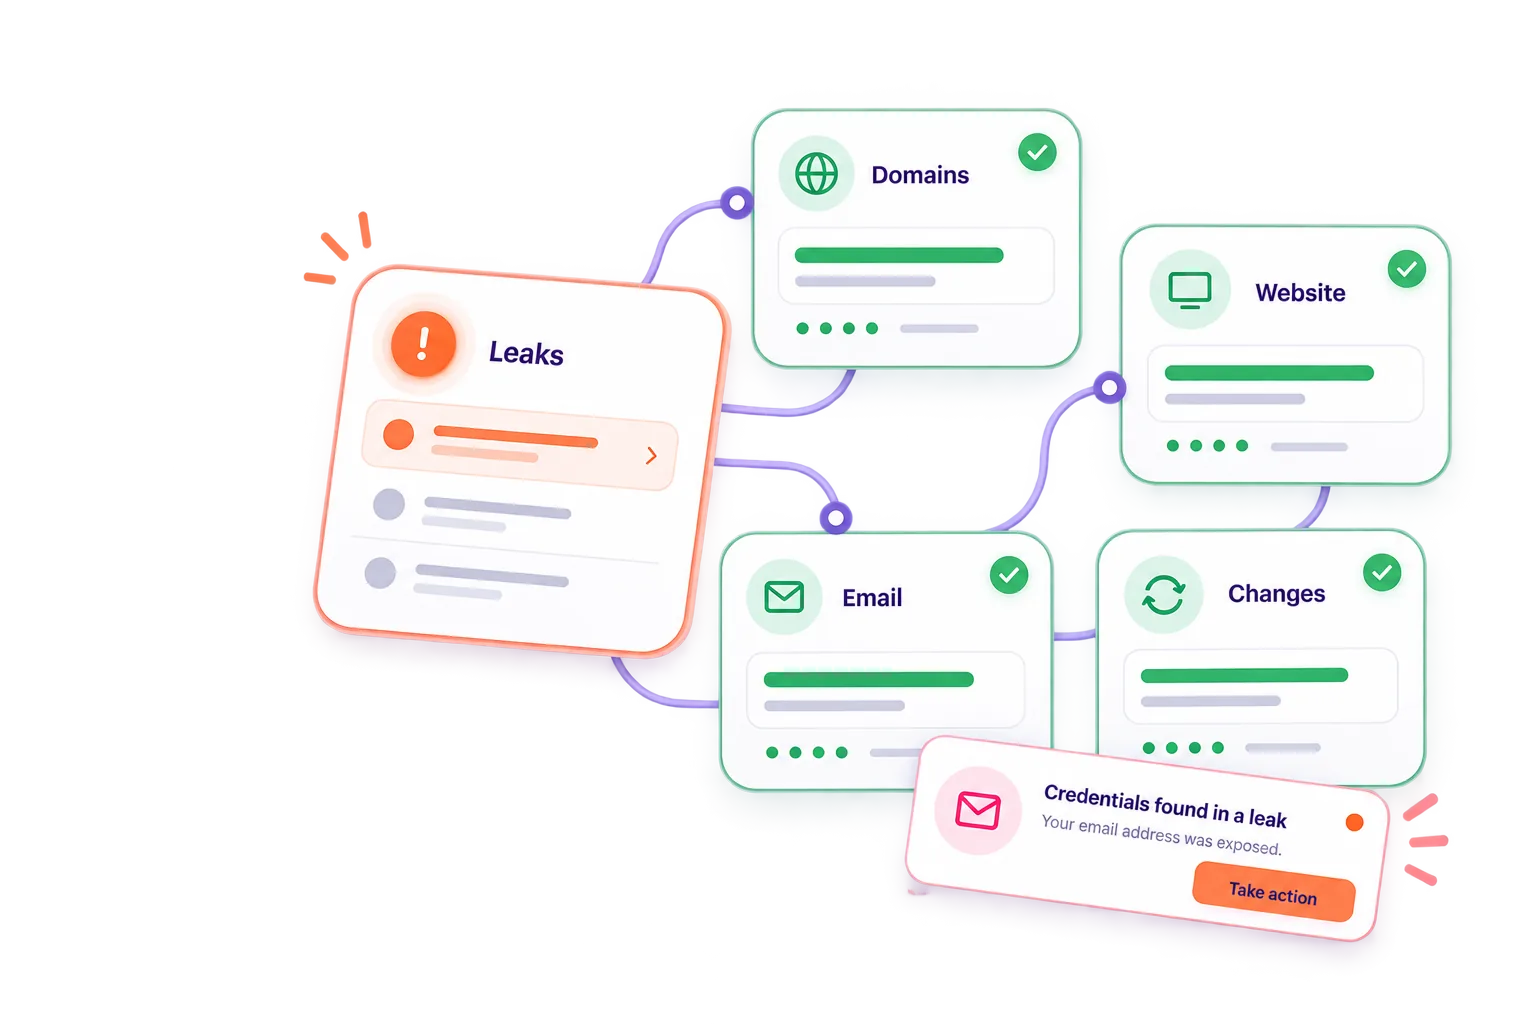
Built for organizations that want continuous security monitoring without running their own security operation.
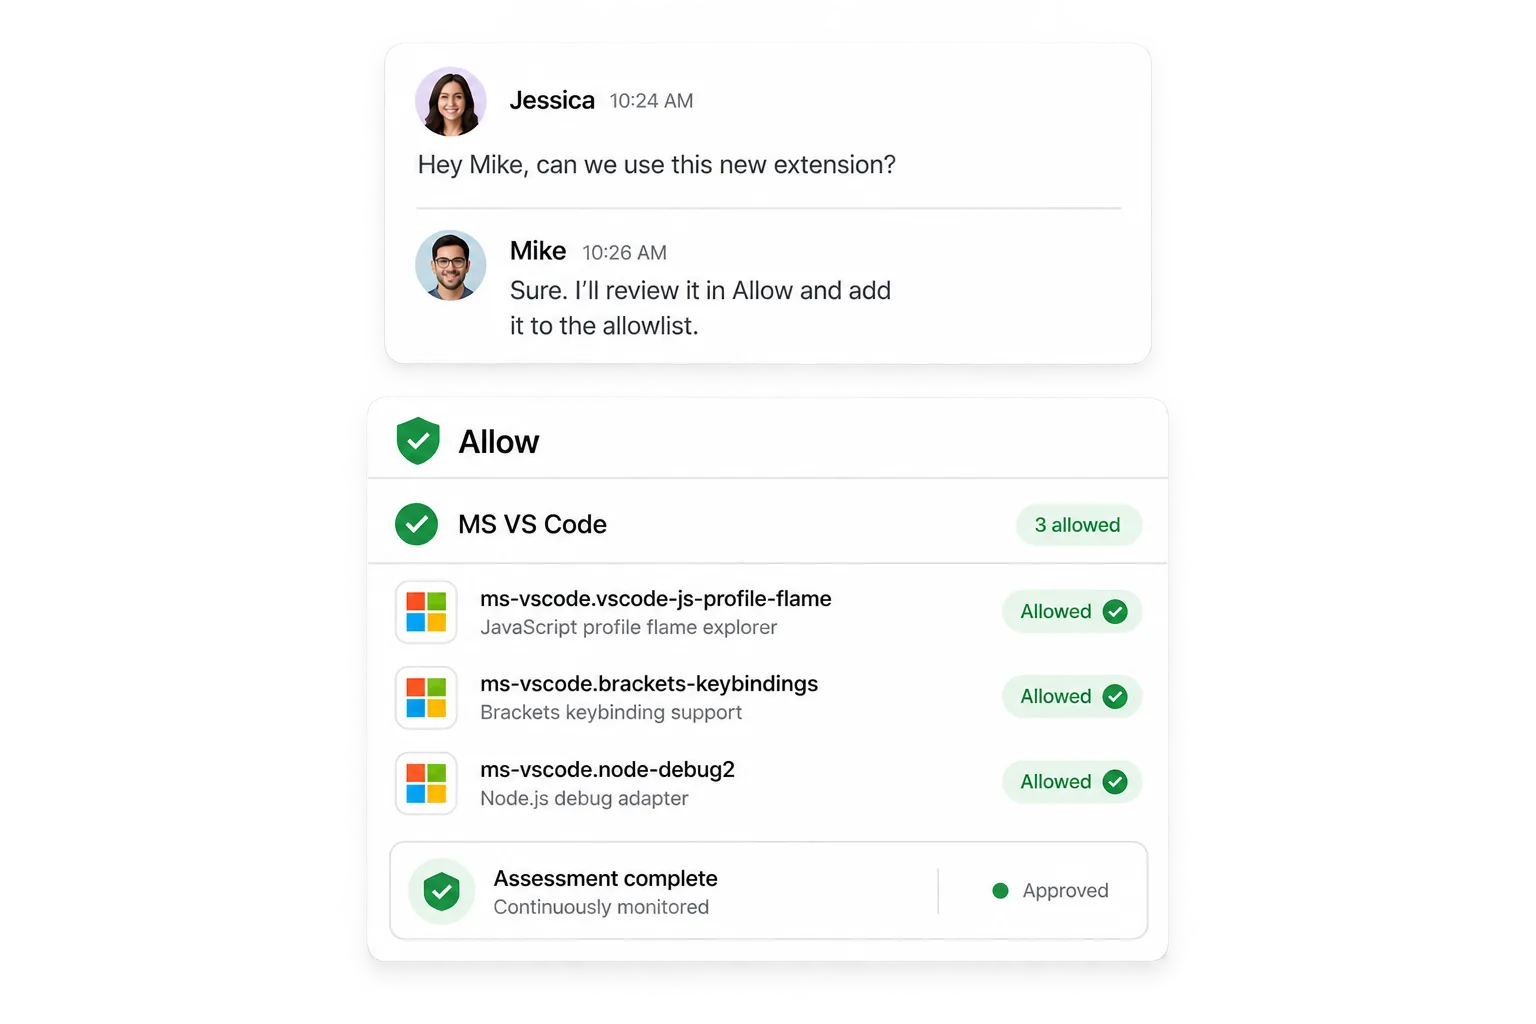
Allow gives security teams a repeatable way to assess, approve and keep watching browser and developer-tool extensions.
For organizations that need extension governance without replacing their existing endpoint-management tools.
Targeted technical work for application and product teams, delivered with reproducible findings and practical next steps.
For engineering teams that need focused expertise for an assessment, review or security improvement programme.
Penetration testing, code review and architecture work for applications and engineering teams.
OWASP SAMM assessments and practical improvement roadmaps for software development organizations.
Code Guardian combines offensive security, security software engineering and practical security leadership. That experience shapes how we build our products: focused, usable and grounded in real security work.
About Code GuardianA seemingly normal scanner email hid a malicious SVG. Here is how we analyzed it and what it teaches about quiet, low-friction attacks.
Read articleCVSS is valuable, but context matters more. See how environmental factors change real-world prioritization.
Read article